Honeypots vs Modern Cyber Deception: Why Decoys Are Evolving
Part of our guide to deception technology
Honeypots were the first generation of cyber decoys. Modern deception goes further, using realistic synthetic assets to engage attackers, reveal intent, and protect real systems before damage spreads.
Honeypots were one of the earliest examples of deception in cybersecurity.
The idea was simple: create a fake system that looks valuable, wait for an attacker to interact with it, and monitor what happens. Since no legitimate user should be touching that fake system, the interaction becomes a strong signal of suspicious activity.
That idea still matters. But modern cyber deception has evolved far beyond a single fake server sitting inside a network.
Today’s attackers move through cloud environments, identities, endpoints, file shares, SaaS tools, and internal applications. They do not always trigger obvious alerts. Often, they quietly test credentials, scan systems, and move laterally toward higher-value assets.
What is a honeypot?
A honeypot is a fake system or resource designed to attract attackers. In simple terms, a honeypot is bait.
It might look like a fake server, fake database, fake login portal, fake file share, or fake vulnerable application. The attacker thinks they have found something useful. In reality, the environment is controlled and monitored.
If someone interacts with it, security teams can investigate with higher confidence because normal users should not be there.
Why honeypots are useful
Honeypots reduce ambiguity.
A normal security alert can be hard to interpret. It may be malicious, or it may just be unusual but legitimate activity. A honeypot is different. If a fake system is touched, that interaction is immediately meaningful.
They can help teams detect unauthorized activity, observe attacker behavior, collect information about tools and techniques, and understand what attackers are looking for.
Where honeypots fall short
The problem is that traditional honeypots can be narrow.
A single fake server may catch some activity, but modern attackers do not always walk into obvious traps. They may use stolen credentials, legitimate tools, cloud services, or identity-based paths that look normal on the surface.
Once attackers gain access, they often move deeper into the environment to find sensitive data, privileged accounts, or critical systems. This is known as lateral movement.
So the challenge is not just creating one fake system. The better question is whether defenders can create believable deception across the places attackers actually move.
What is modern cyber deception?
Modern cyber deception is the broader strategy of placing believable fake assets, signals, credentials, identities, and environments across an organization.
Instead of relying on one isolated trap, deception can include decoy servers, fake credentials, synthetic identities, deceptive files, fake admin portals, decoy databases, synthetic cloud resources, and controlled attacker engagement environments.
The goal is not only to catch an attacker touching one fake machine.
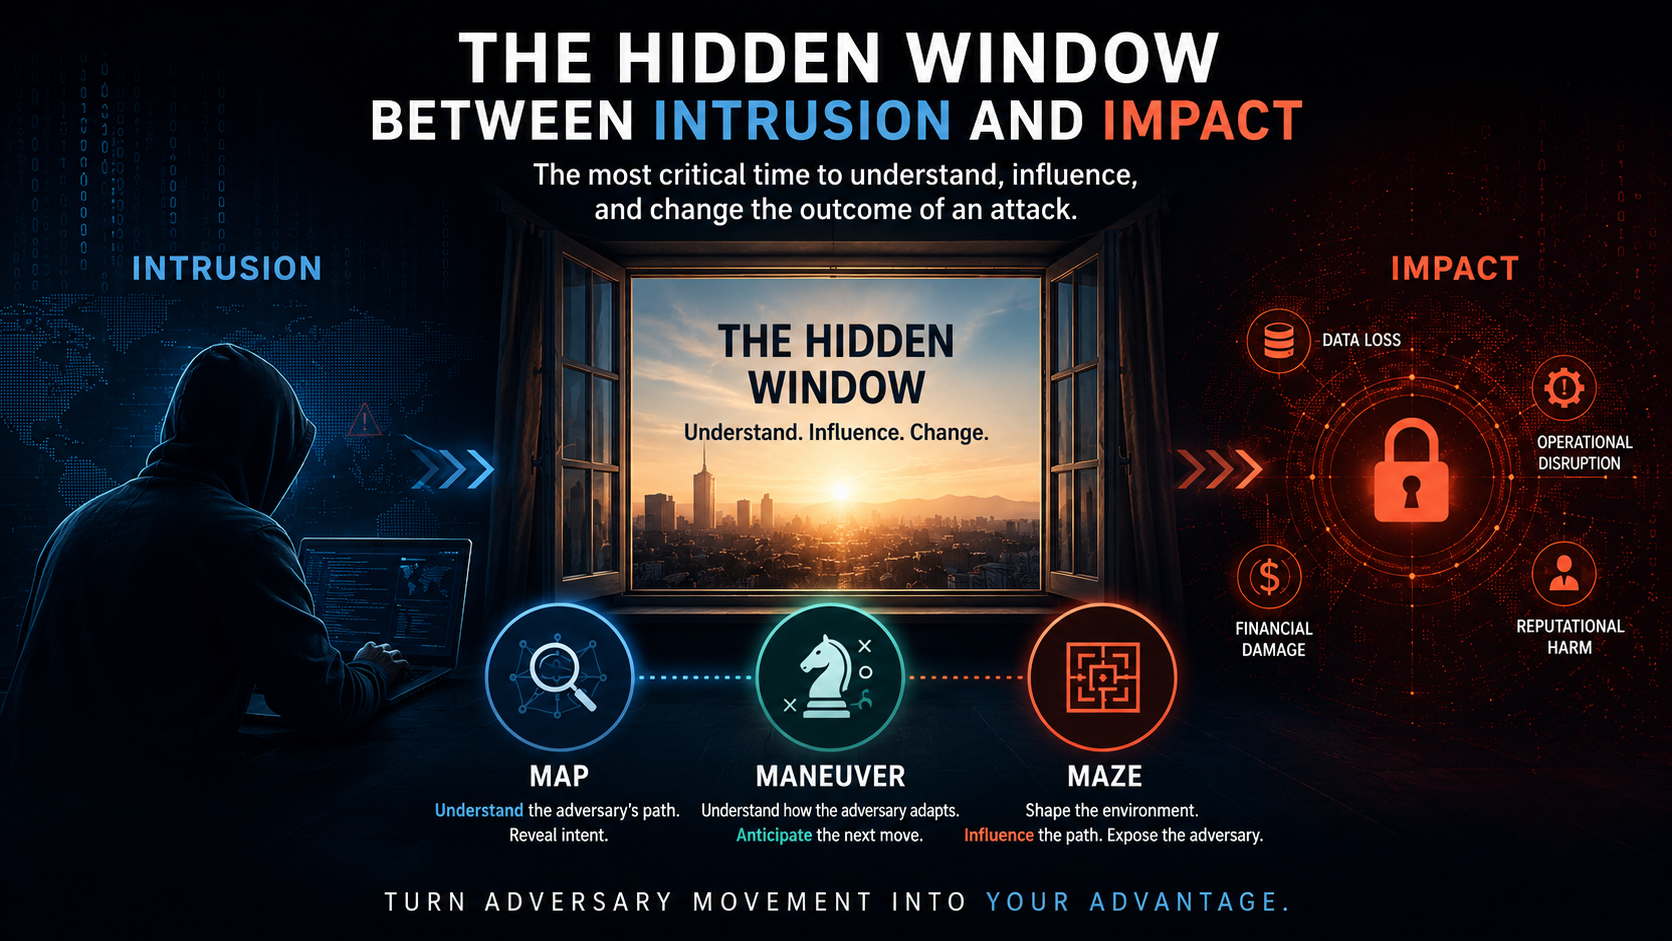
The goal is to shape the attacker’s path, guide them toward controlled assets, and turn their behavior into intelligence.
Why this matters for lateral movement
The first compromised system is rarely the attacker’s final target.
After getting inside, attackers may search for credentials, scan internal services, test access to file shares, or move from one system to another. This activity can be hard to separate from normal behavior.
Modern deception gives defenders a way to create high-confidence tripwires inside that movement.
A fake credential, synthetic file share, decoy admin portal, or synthetic server can reveal what an attacker is interested in and where they may be trying to go next.
At MirrorMire, we use the term Synthetic Cognitive Agents, or SCAs, to describe advanced deception assets that go beyond traditional honeypots.
A traditional honeypot is usually a fake system. A Synthetic Cognitive Agent is designed to behave more like a believable digital asset inside a controlled environment. It can attract attacker attention, support engagement, and help defenders understand what the attacker is trying to do.
Deception is not a replacement for existing tools
Cyber deception should not replace EDR, SIEM, XDR, identity security, cloud security, or zero trust controls. It works best as an added layer.
Existing tools help detect malware, suspicious behavior, policy violations, and abnormal activity. Deception adds something different: controlled assets where attacker interaction itself becomes meaningful. That gives security teams better signals, not just more alerts.
Honeypots introduced an important idea: attackers can be misled. But modern enterprise environments are too complex for deception to remain limited to one fake server.
Cyber deception has evolved into a broader strategy that uses synthetic assets, deceptive signals, and controlled engagement environments to detect attackers earlier, reveal intent, and protect real systems before damage spreads.
Honeypots were the beginning.
Modern cyber deception is the next step.
See how MirrorMire approaches modern cyber deception.
Explore how AMazeTM uses Synthetic Cognitive Agents, deceptive signals, and attacker engagement to help security teams detect movement earlier and turn adversary behavior into actionable intelligence.
Sources
- NIST Computer Security Resource Center, Honeypot definition
https://csrc.nist.gov/glossary/term/honeypot - CrowdStrike, What is lateral movement?
https://www.crowdstrike.com/en-us/cybersecurity-101/cyberattacks/lateral-movement/ - MITRE ATT&CK, Adversary tactics and techniques knowledge base
https://attack.mitre.org/ - NIST Special Publication 800-207, Zero Trust Architecture
https://nvlpubs.nist.gov/nistpubs/SpecialPublications/NIST.SP.800-207.pdf