How Deception Technology Reduces False Positives
Part of our guide to deception technology
Deception technology reduces false positives by using fake assets that legitimate users ignore but attacker's target. This makes alerts far more accurate, meaningful, and actionable for security teams.
Most security teams today are overwhelmed with alerts. The real challenge isn’t just detecting threats - it’s figuring out which alerts actually matter. Analysts spend hours chasing activities that turn out to be harmless, while real attackers continue moving quietly through the network.
Deception technology changes that experience completely.
Instead of relying only on patterns, signatures, or suspicious behavior, deception creates realistic traps inside the environment - systems, credentials, files, and assets that no legitimate employee should ever interact with. So, when someone touches them, it immediately stands out.
That’s what makes deception so powerful from a human perspective: security teams no longer have to sift through endless noise hoping to find the real threat.
Every alert becomes more meaningful. Every investigation becomes faster. And analysts can focus their energy on actual attacks instead of alert fatigue.
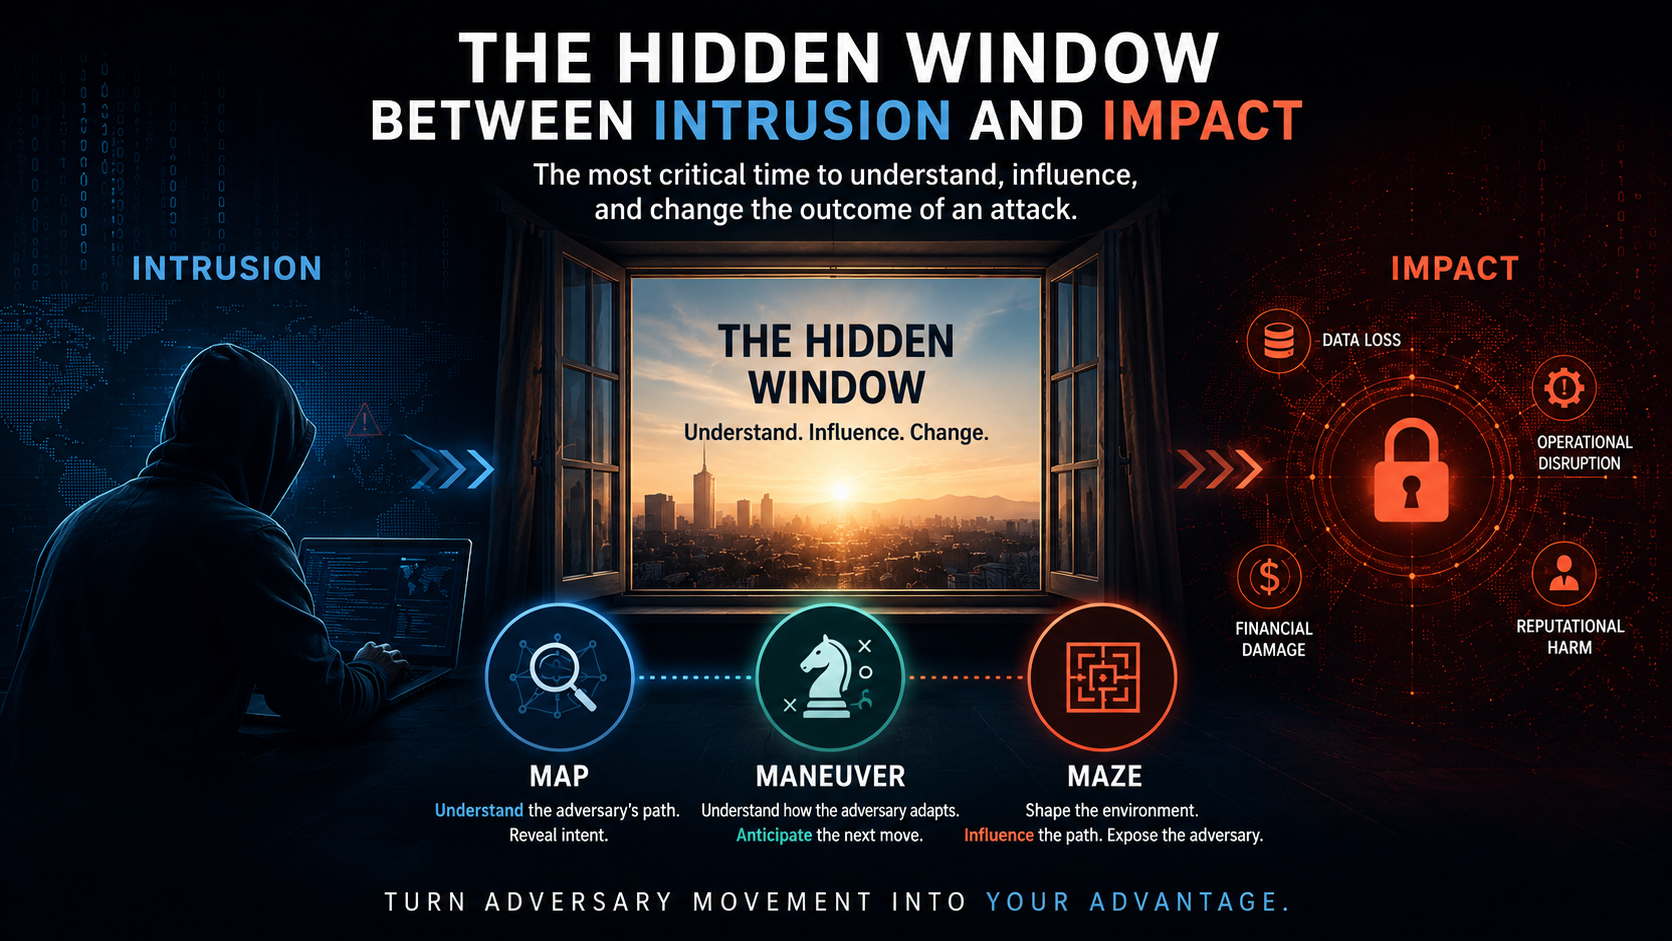
It also helps organizations detect attackers much earlier in the kill chain. Threat actors often spend days or weeks exploring a network before launching an attack. Deception exposes that behavior in real time, often before any damage is done.
At its core, deception technology brings clarity back to cybersecurity. It helps security teams work smarter, respond faster, and spend less time questioning whether an alert is real - because in a deception environment, interactions are rarely accidental.